Orbis Shield
Orbis Shield is the ROUNDBOX Orbis threat‑intelligence service. It tells you — in one call or one click — whether a message, file, URL, domain, or IP address is malicious, and why. Use it from the branded console or straight from your own systems through a metered API.
Shield combines multiple detection engines and reputation sources behind a single ROUNDBOX verdict, so you get one clear answer (Clean / Suspicious / Malicious) with a confidence score and the evidence behind it — no need to stitch together a dozen feeds yourself.
What you can check
| Capability | What it answers | Where |
|---|---|---|
| Message inspection (antispam / antiphishing) | Is this SMS, WhatsApp, or email message spam or a phishing attempt? | Console · POST /api/v1/antispam |
| Malware analysis | Is this file malicious? Static analysis, a dynamic behavioural sandbox, and hash reputation. | Console · POST /api/v1/files, /api/v1/files/dynamic, /api/v1/files/hash |
| URL analysis & web sandbox | Is this link safe to open? Reputation plus live detonation. | Console · GET /api/v1/urlsearch |
| DNS & IP reputation | Is this domain or IP address associated with threats? | Console · GET /api/v1/dnssearch, /api/v1/ipsearch |
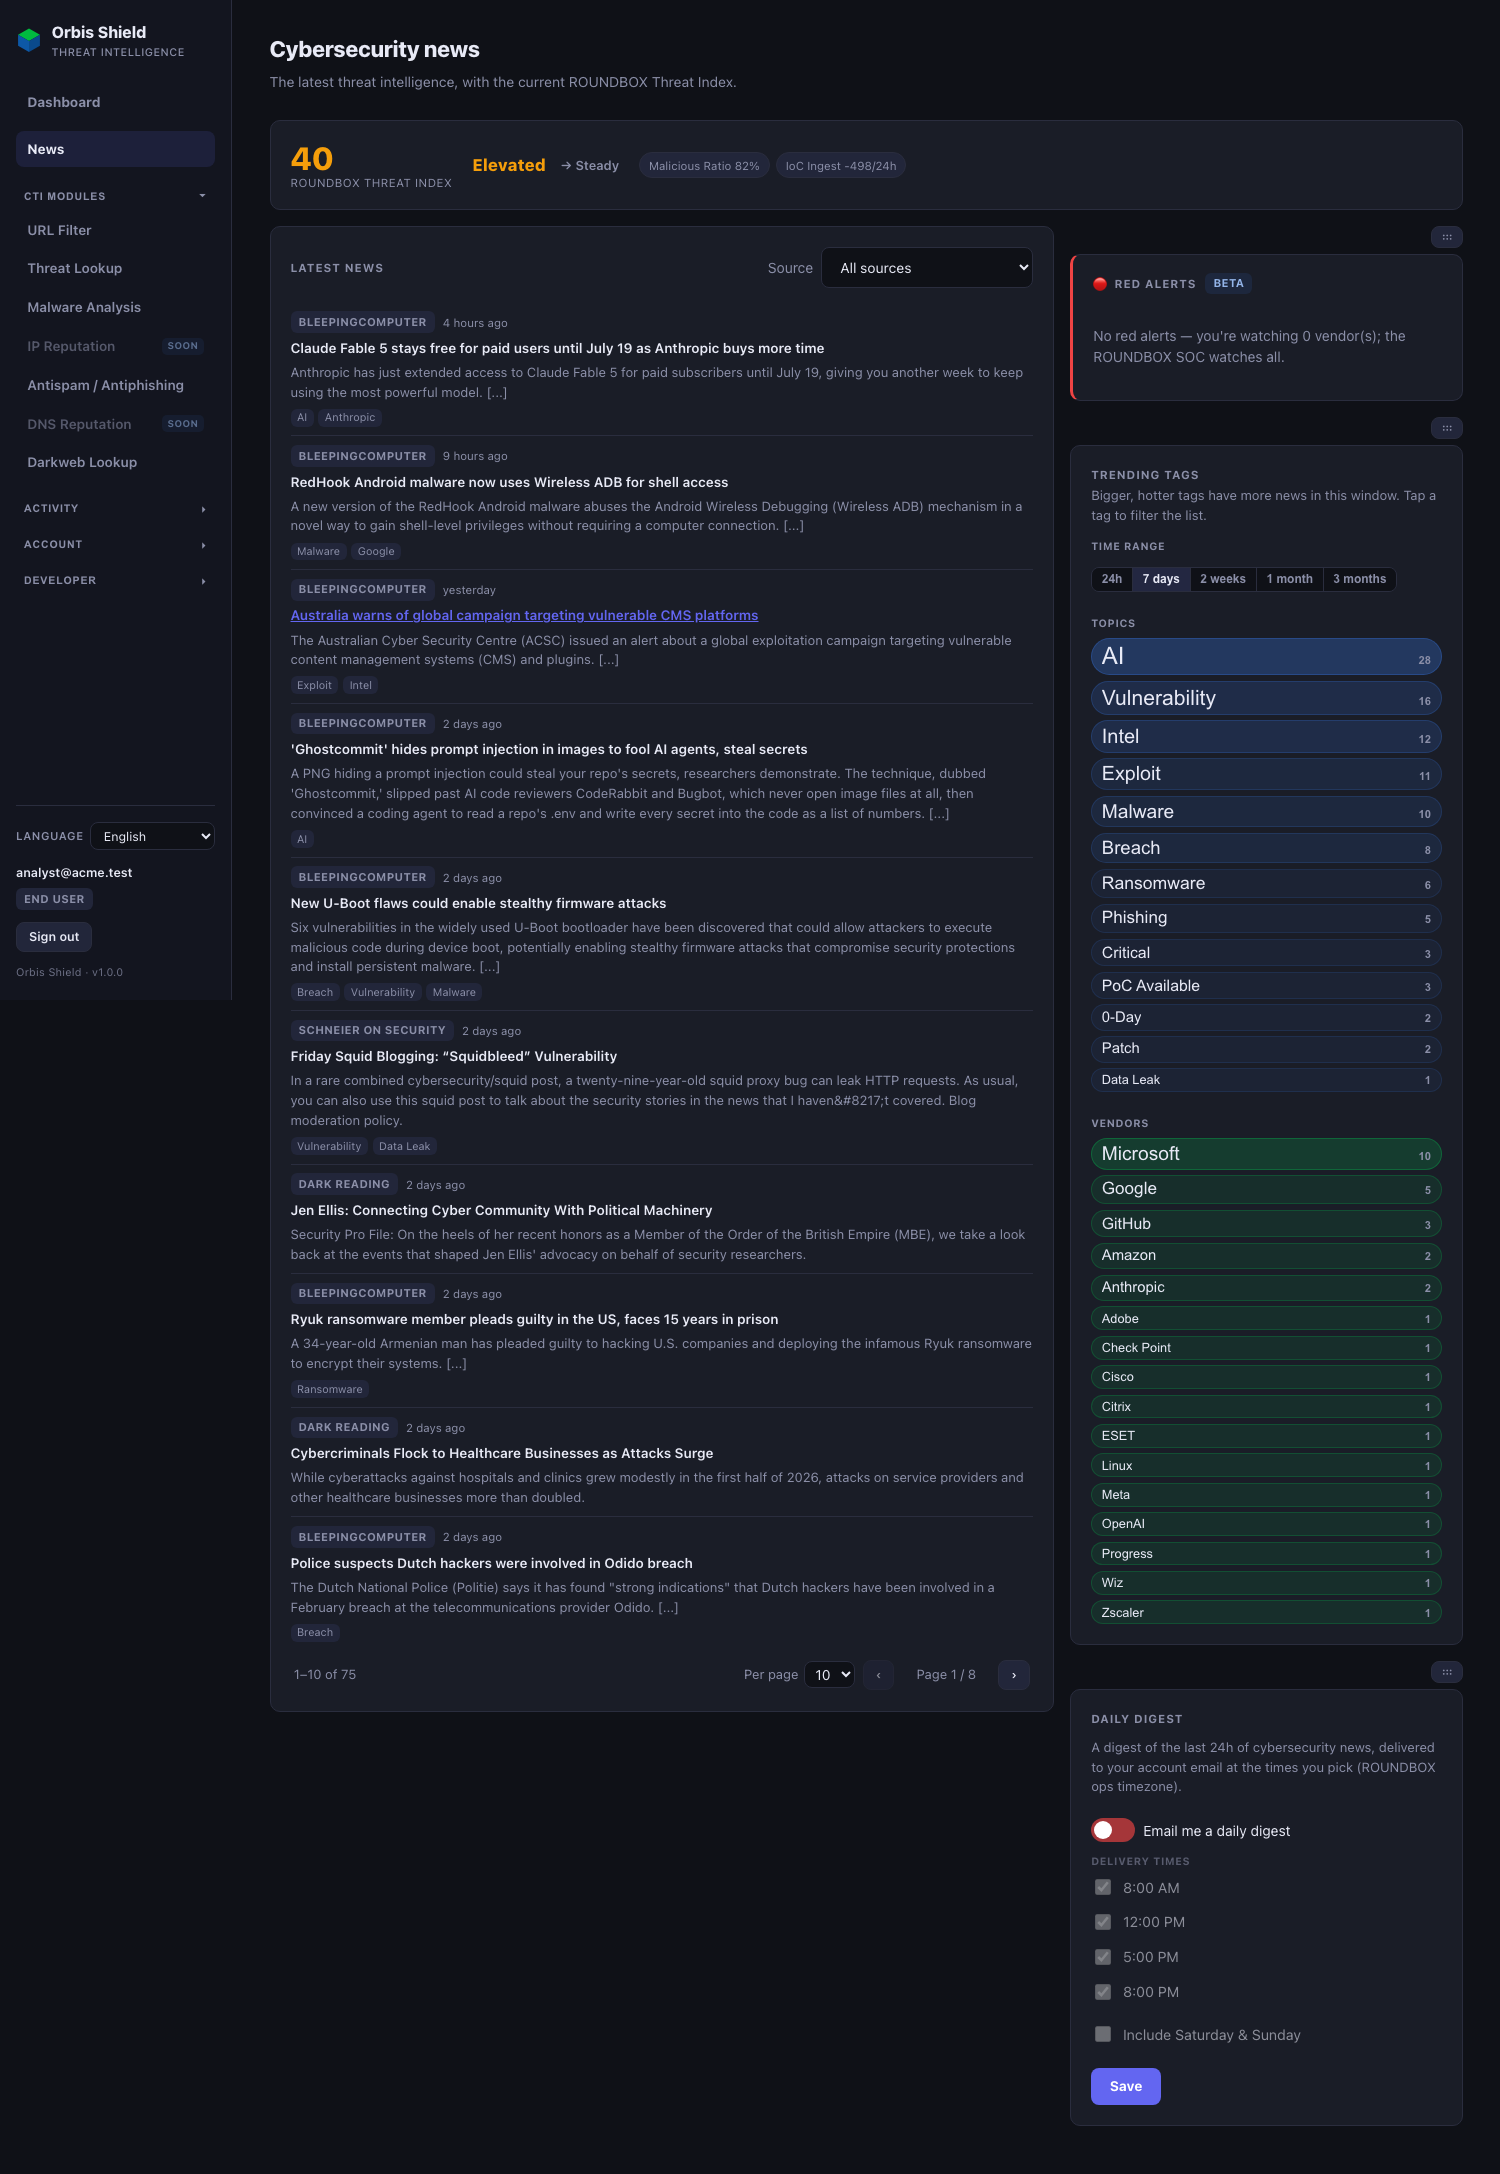
| Threat intelligence news | What is happening right now, and does it affect vendors you rely on? | Console (news, Red Alerts, ROUNDBOX Threat Index) |
Two ways to use it
- The console — a branded web app for analysts: run lookups and scans, read results, follow the threat‑intelligence news feed, and manage your team's API keys and webhooks.
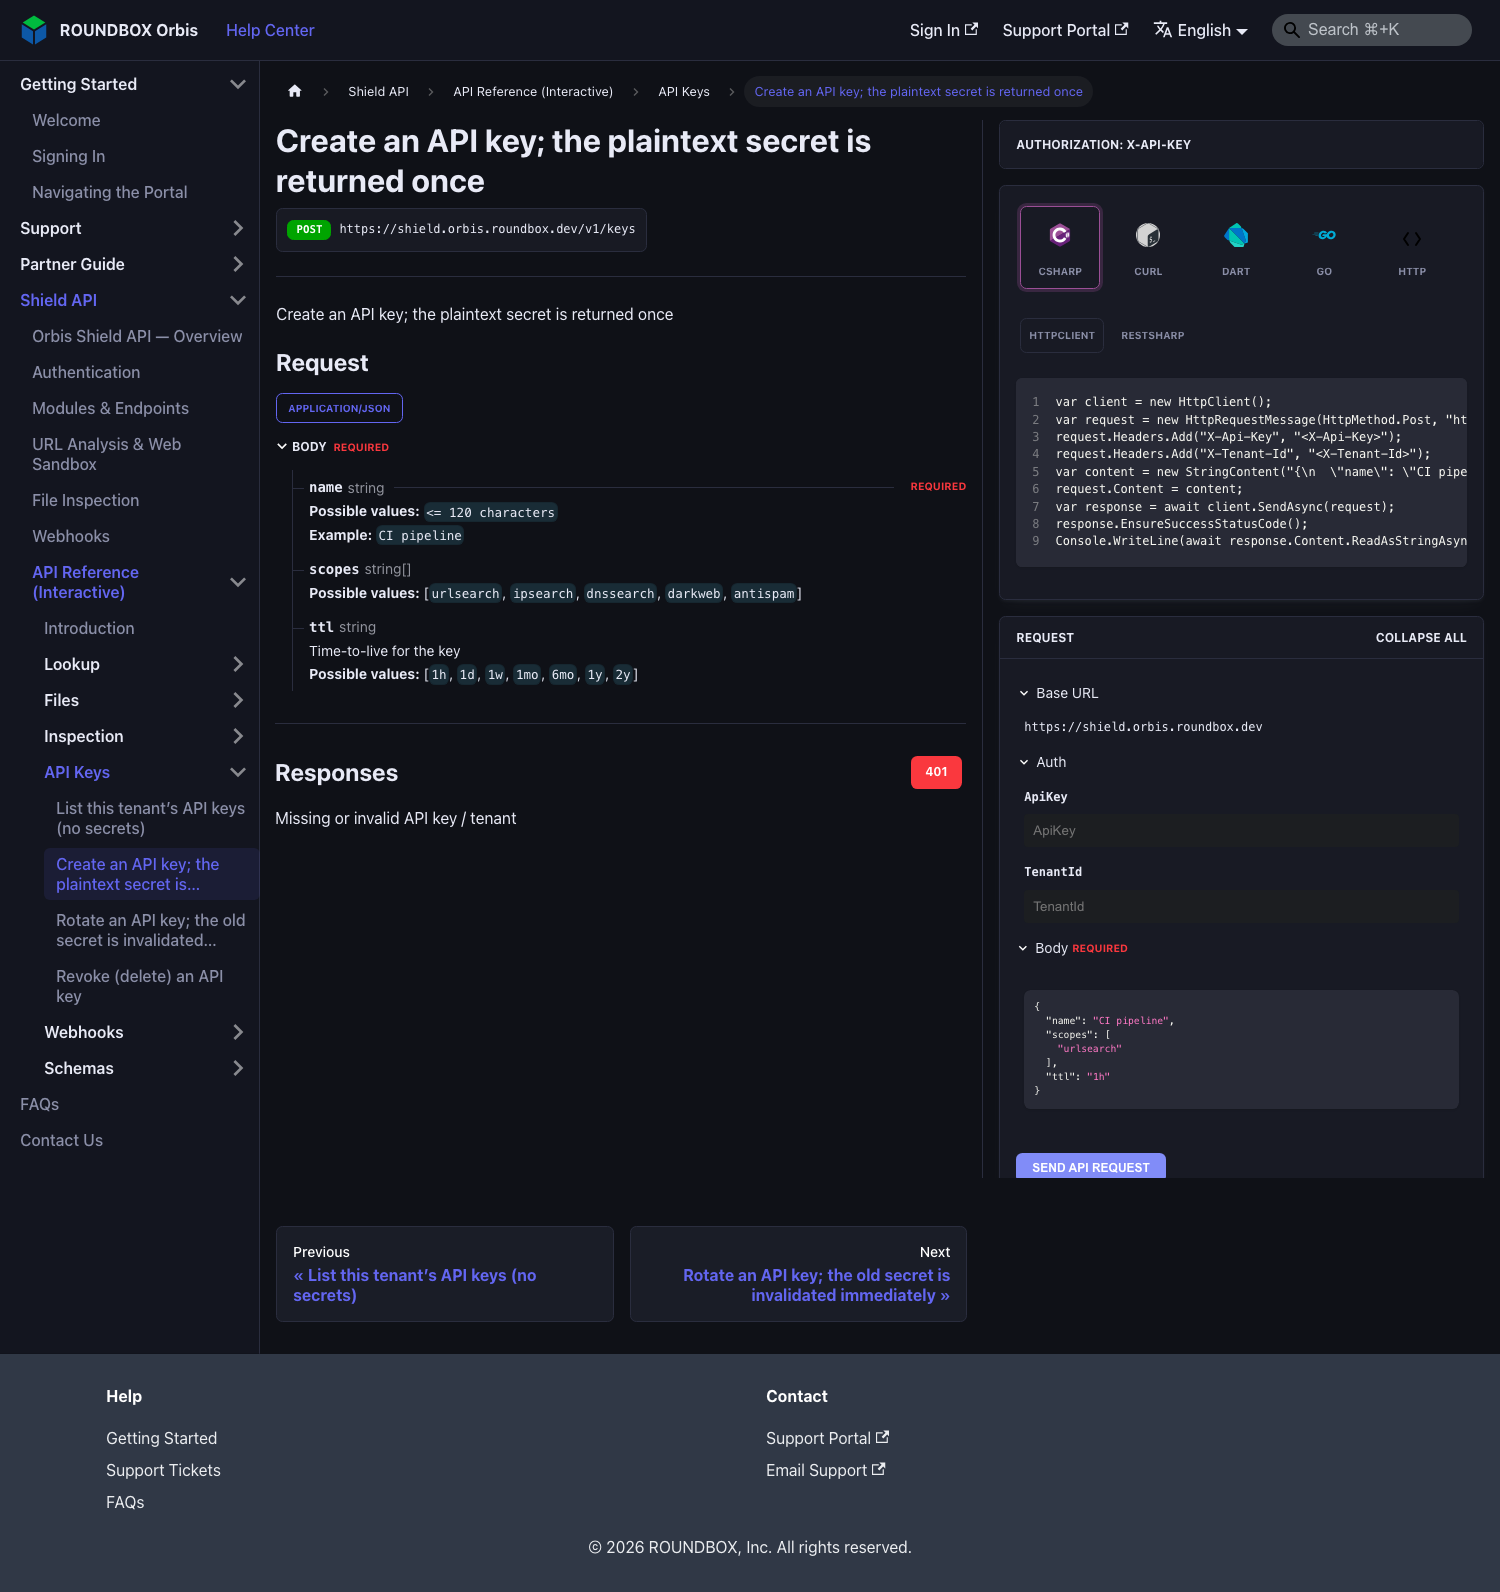
- The API — a metered REST API for wiring Shield into your own gateways, SIEM enrichment steps, or automation. Authenticate with an API key, submit an artifact, and get a normalized verdict back. See the API section and the interactive API Reference, where you can try every endpoint from the browser.
A single, explainable verdict
Every result rolls up into one ROUNDBOX verdict with a score and a short list of key findings, so an analyst — or an automated rule — can act immediately. Files that warrant it are run through a behavioural sandbox; messages flow through a layered inspection pipeline; lookups draw on curated reputation intelligence. What you see is the conclusion and the evidence, not the plumbing.
Getting started
- Sign in to the console, or create an API key under Developer → API keys.
- Run your first check — upload a file under Malware Analysis, or call
GET /api/v1/ipsearch?value=…. - Wire results into your workflow with webhooks.
See Authentication for API keys and request signing, and the API Reference for the full, tryable endpoint catalog.